Reinforce your most critical security layer: the human factor
No matter how sophisticated the technology, 90% of cyber attacks start with human error. We test your employees' cyber awareness with real-world scenarios. Our goal is not just to find out "who clicked". It's to sharpen your organization's reflexes against cyber incidents and turn your people into a true "Human Firewall."
Audit and Compliance: This service is aligned with KVKK Training and Awareness articles, ISO 27001 Information Security Awareness (A.7.2.2) and BDDK personnel awareness testing.
Attackers don't only use email, and we audit every communication channel.
Tailored to your organization and employee roles: believable, technically sophisticated email scenarios.
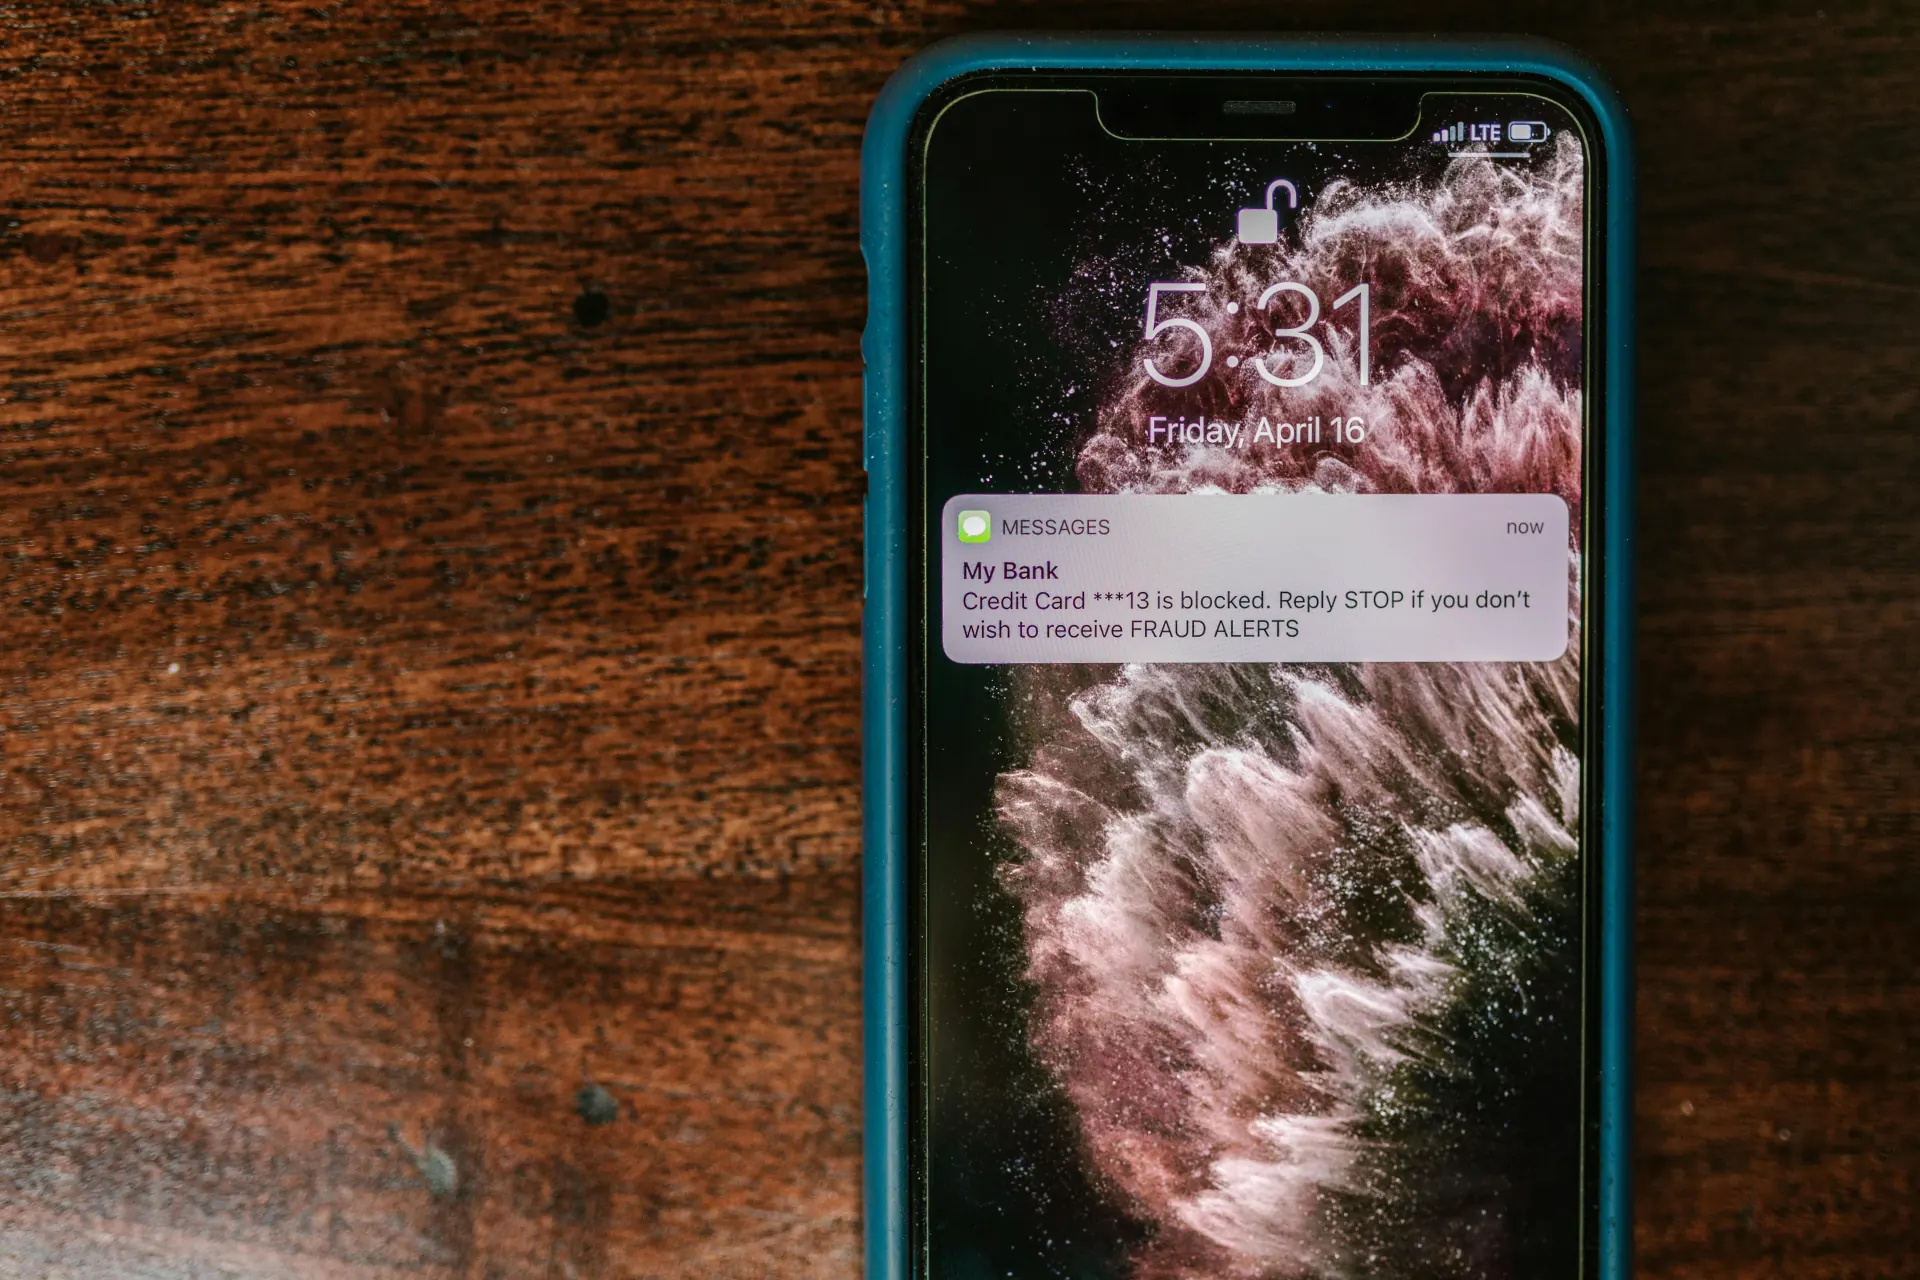
Psychologically-driven manipulation attacks carried out by phone and SMS.
Bypassing your organization's physical security through the human factor.
An employee who falls for phishing immediately receives interactive feedback and is automatically assigned to the relevant awareness module on Raze Academy. Not punishment, a learning trigger.
From Simulation to Training
A user who falls into the trap immediately sees an interactive "Why and How?" alert, afterwards they're automatically assigned to a role-specific awareness module. Periodic tests measure your organization's Awareness Index, reported on a regular cadence.
An employee who falls into the trap immediately sees a "Why and How?" alert. They're then automatically assigned training through Raze Academy. Periodic tests report growth in your organization's "Awareness Index."
Targeted phishing, vishing, smishing and physical social-engineering combinations with tailored scenarios.
Get a quoteOSCP, OSCE certified. GDPR/KVKK-compliant target management and realistic campaigns within ethical limits.
View certificationsDrive lasting behavioral change with role-based awareness training after the campaign.
ExploreNo. For a realistic measurement, the campaign is run with the knowledge of management and designated points of contact only.
No. Reporting is anonymized at department and role level. The goal is to measure and improve organizational awareness, not to punish individuals.
Yes. Scenarios are designed together with your legal team from a personal data processing perspective. Collected data is kept to a minimum and securely destroyed after the campaign.
All communication channels including email (spear phishing), phone (vishing), SMS (smishing) and physical scenarios (baiting, tailgating).
We recommend quarterly or semi-annual campaigns for lasting behavioral change. Progress is measured with trend reports.

 EN