
 EN

 Regulation
04 JUN 2026
Raze Security is a technology company holding the TSE A-Level authorization certificate, delivering end-to-end expertise in enterprise cybersecurity. With our certified experts, internationally recognized methodologies and proprietary security platforms, we secure the digital resilience of organizations within a measurable, transparent and sustainable framework.
Our certified expert team offers deep expertise in adversarial simulation, application security and infrastructure hardening. Actionable findings, transparent reporting and processes aligned with KVKK, BDDK and ISO 27001.
 01
End-to-end, prioritized security assessments and clear action plans for networks, web, mobile and APIs.
 02
Deep code review identifying complex vulnerabilities beyond OWASP using manual and automated analysis across 20+ programming languages.
 03
Realistic attack simulations based on MITRE ATT&CK to test SOC, incident response and organizational resilience.
 04
A continuous security service that consolidates and prioritizes vulnerabilities, manages them under SLAs, and reports steady risk reduction.
 05
Controlled DDoS simulations that test infrastructure capacity, CDN, WAF and rate-limit controls, paired with hardening recommendations.
 06
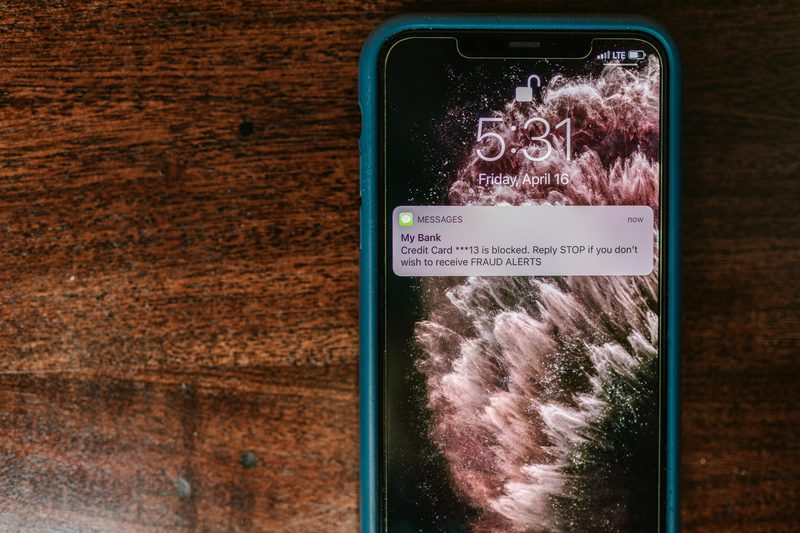
Targeted phishing, vishing, SMS and impersonation scenarios that measure employee awareness and human-layer security.
 07
Role-based, hands-on training tailored to your teams in areas such as secure coding, incident response and threat modeling.
 08
Physical security testing at corporate facilities to assess access controls, monitoring systems and physical intrusion risks.
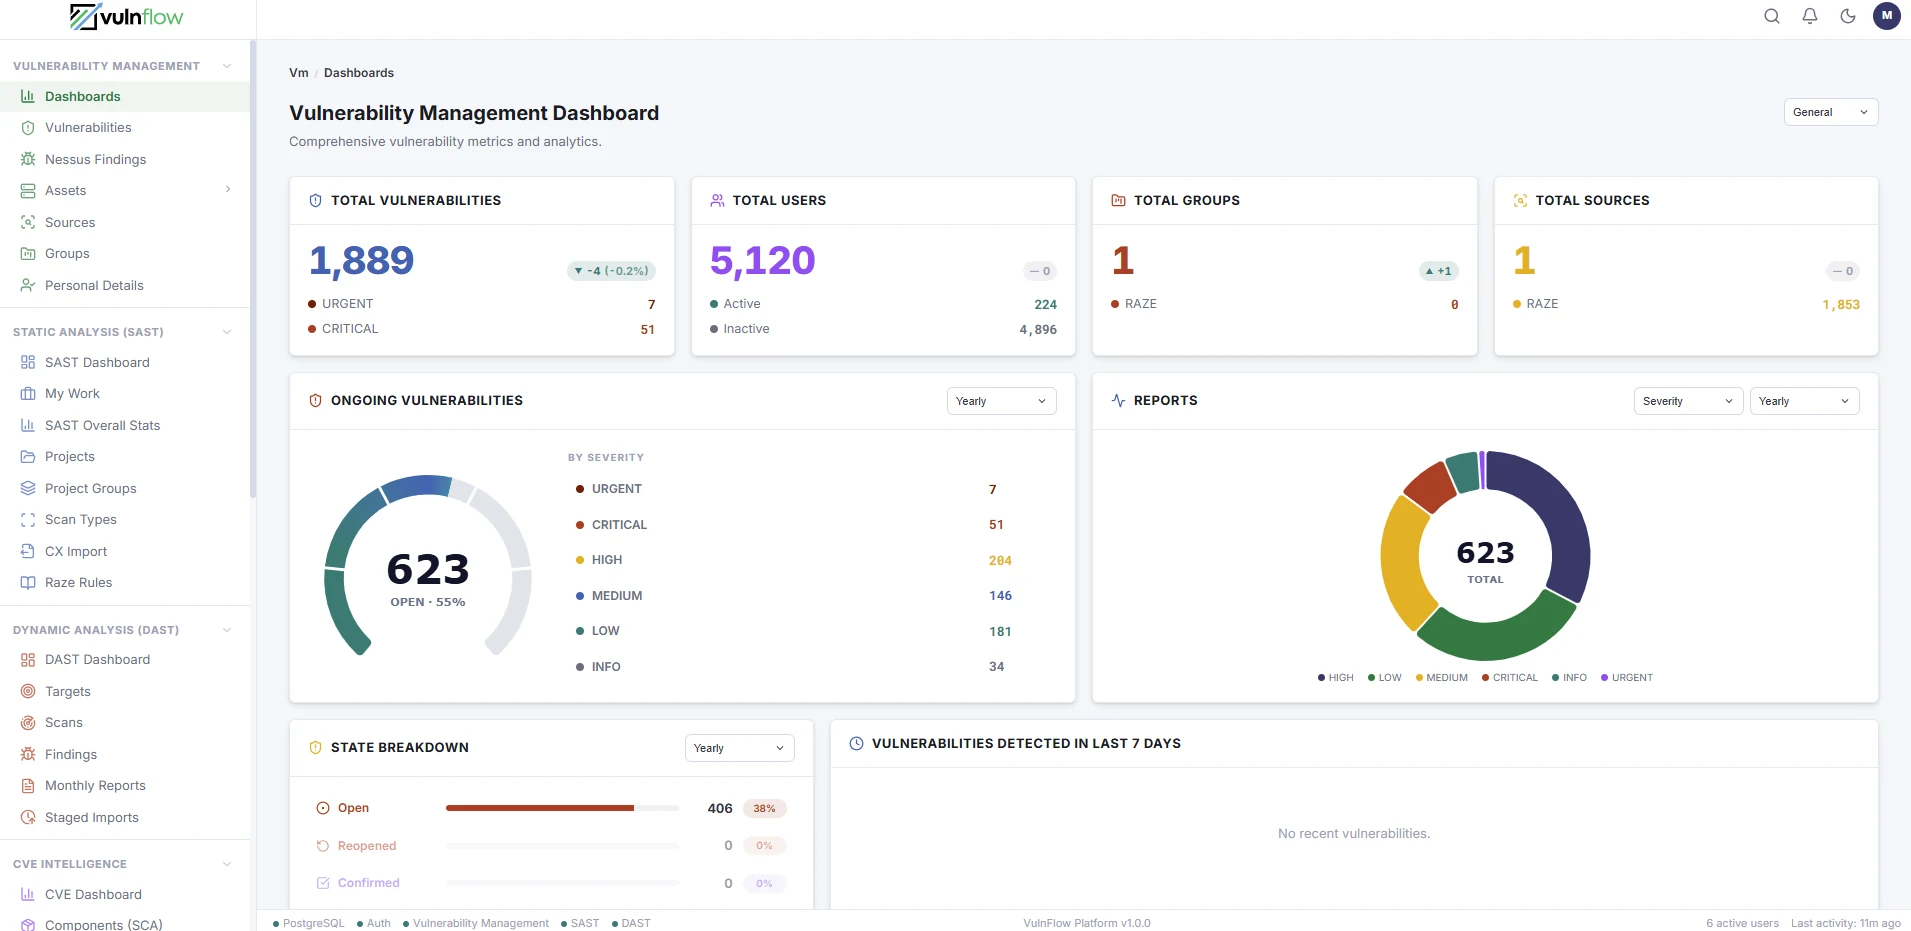
Two purpose-built platforms covering the full scope of enterprise security operations. vulnflow consolidates findings from all sources (SAST, DAST, SCA, external attack surface scans, penetration testing and VulnCrypt) into a single hub. This delivers your teams unified visibility, from source code to infrastructure and from cryptographic assets to the external attack surface.
Unified Findings and Vulnerability Management
Consolidates findings from SAST, DAST, SCA, penetration tests, bug bounty programs and external attack-surface scanners into a single platform. Business-context risk prioritization enriched with asset criticality, network exposure and active threat intelligence, paired with SLA-based remediation tracking. Bi-directional sync with Jira, GitHub, GitLab and ServiceNow.
Cryptographic Asset Management
Centralized discovery, analysis and management of TLS/SSL certificates, SSH keys, exposed secrets and AD CS misconfigurations. Deterministic 14-factor risk scoring backed by machine-learning anomaly detection. On-premises, air-gapped and hybrid deployment options.
OSCP, OSCE, CRTO and OSEP certified professionals with deep field experience in offensive security and enterprise environments.
View certificationsSolutions tailored to organizations of every scale, sector-specific needs and regulatory requirements. Full alignment with national and international standards, including KVKK, BDDK and ISO 27001.
View complianceBeyond consulting alone. Our security platforms work in tandem with our services to deliver continuous visibility and measurable risk reduction.
View servicesOne of Türkiye's highest-tier authorized domestic cybersecurity companies. Certified assurance for critical infrastructure and regulated organizations.
About us
Regulation
 Threat & Trend
 Governance
 Penetration Testing
 Red Team
 Technical
 Technical
 DFIR
 Law-Technology
 Research
 Threat Intelligence
 Technical Analysis